How Obsidian Security Defends SentinelOne
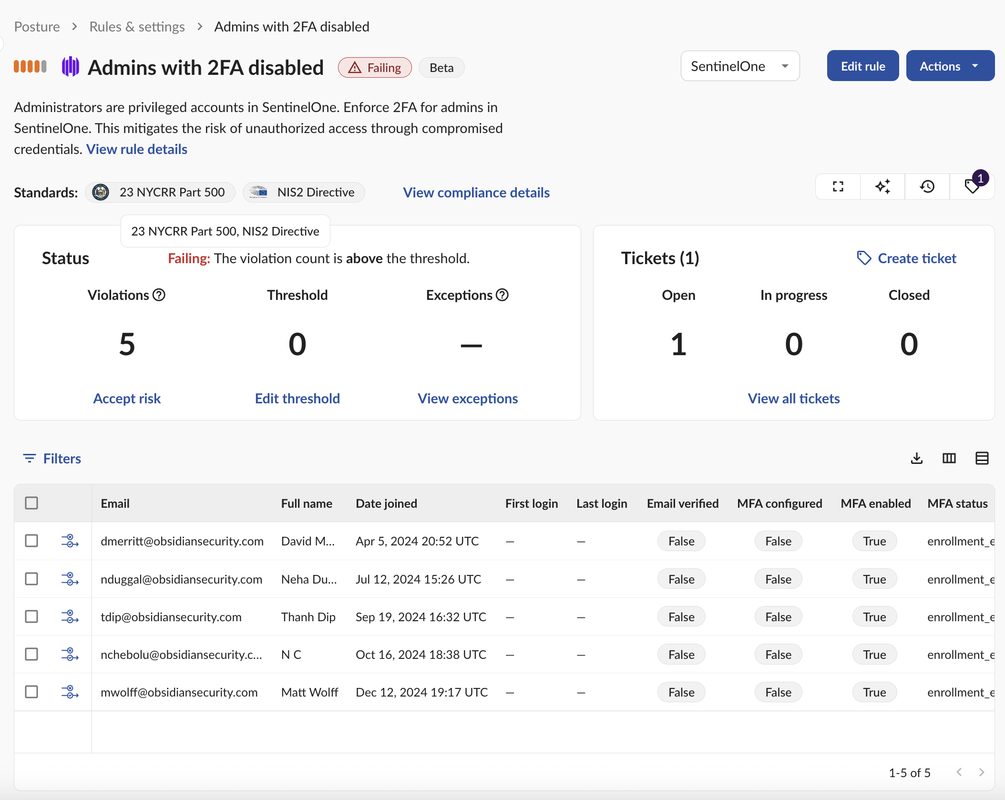
- Continuously enforce secure SaaS configurations: Obsidian scores configurations based on criticality according to built-in or custom policies and flags high-priority failures.
- Prioritize instantly with evidence-based posture alerts: Reduce business friction while minimizing unacceptable risk within a unified interface.
- Right-size privileged access and SaaS integrations: The Obsidian Knowledge Graph unifies identity across SaaS to flag weak MFA, inactive accounts, shadow admins, and overly broad scopes, human or non-human.
- Automate SaaS audits to easily prove compliance: Track SaaS posture in real time and map controls to frameworks like SOC 2, ISO 27001, CIS, and NIST.
Free Trial