HEAD-TO-HEAD
Noma vs. Obsidian
Noma watches the agent. The breach plays out in Salesforce, Workday, and your third-party apps.
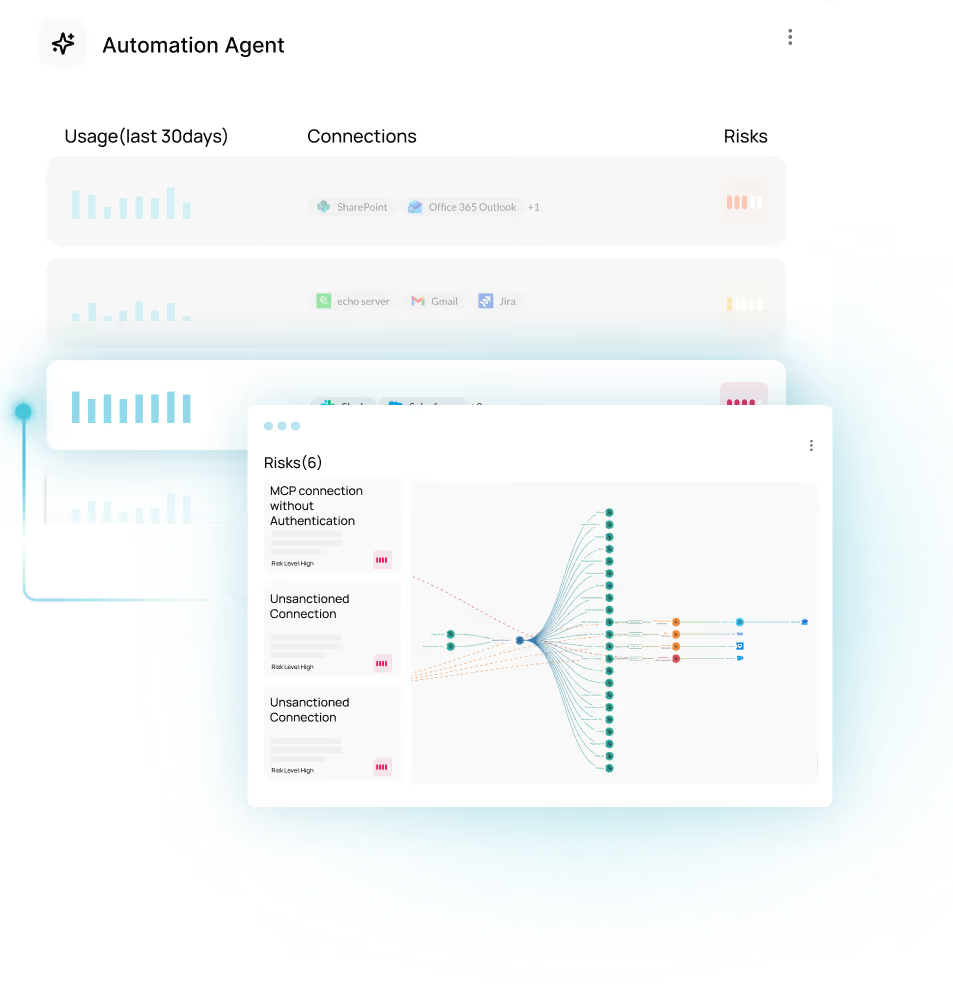
Noma watches the agent. The breach plays out in Salesforce, Workday, and your third-party apps.


Both platforms help teams manage AI risk. The difference is the layer each platform prioritizes and the data each one reads.
Both enforce at runtime. The difference is what each policy reads when it fires. Agent-side runtime can control what an agent does at the tool-call level. Obsidian extends runtime decisioning with SaaS state, identity, and permissions, so policies can be more specific over time: for example, don't touch a file in OneDrive labeled sensitive, when the agent was built by a specific user, calling on behalf of a specific identity. That granularity comes from reading the receiving app's state and identity context, not just the agent's tool calls.
Inventory is only the starting point. Obsidian shows who built the agent, who ran it, and what the service account inside the SaaS app is permissioned to do. That gives defenders the context to understand which agents create real business risk and align configuration to that risk.
Noma ships strong out-of-the-box framework mappings for NIST AI RMF, ISO 42001, EU AI Act, and OWASP. The harder question is whether a checklist-passing AI inventory catches the breach. An agent can clear every governance control on paper and still hold a toxic combination of entitlements only visible from inside the connected SaaS apps. Obsidian builds the evidence layer the governance reporting actually needs.
You'd be paying twice for the AI-layer data. Both platforms connect to the same AI platforms with effectively the same connectors and ingest the same underlying telemetry. The cleaner answer is to pick the platform that reads the SaaS and identity context the other can't.
Posture detection tells you an agent looks risky. By the time a posture finding lands, the agent has often already executed. Runtime enforcement fires at the tool call, before the action completes. Both platforms have moved to runtime for this reason. The remaining question is what each runtime can read: agent inputs and outputs alone, or also the SaaS state and identity context that decide whether the action is actually risky.
99.99% uptime over the last 12 months. Regional hosting across the US, Europe, Saudi Arabia, and Australia. Granular RBAC scoped per app. Production-safe connectors with bulk-API support. Obsidian connects to your most critical SaaS apps and collects activity data without disrupting them. Learn more about our certifications and attestations.
These come from real customer environments, including customers who've evaluated Noma and Obsidian.